Docker network schemes
Requirements notes:
- SPAM filters, karma system, relaying itself needs to see real source IP. Many containerised network schemes have problems with losing the real source IP due to packet manipulation. While processing on HTTP(s) ports is designed to be tolerant of not knowing the real IP and can be reverse-proxied, hiding the source IP on core mail server ports can put your mail server in an open relay state.
- If you're using a reverse proxy and want to use free certificates from Let's Encrypt, you'll need to redirect the .well-known folder properly. If your proxy itself issues certificates for other containers, it may be sufficient to share the folder between containers via volume.
- Inbound IP should be the same as outbound or you need to adjust SPF records
- If you don't understand how IPv6 works, it's better not to use it at all, especially if you're using anything other than network=host mode
-
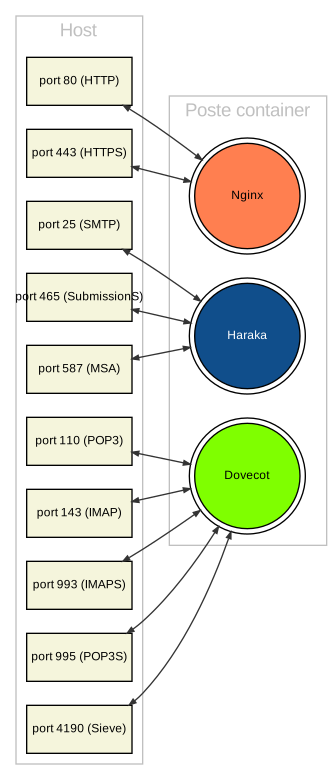
Recommended: dedicated server for poste.io only (network=host)
Yes: IPv4 and IPv6 fully compatible
Yes: compatible with host's iptables firewall
Yes: Let's encrypt certificates working by default
-
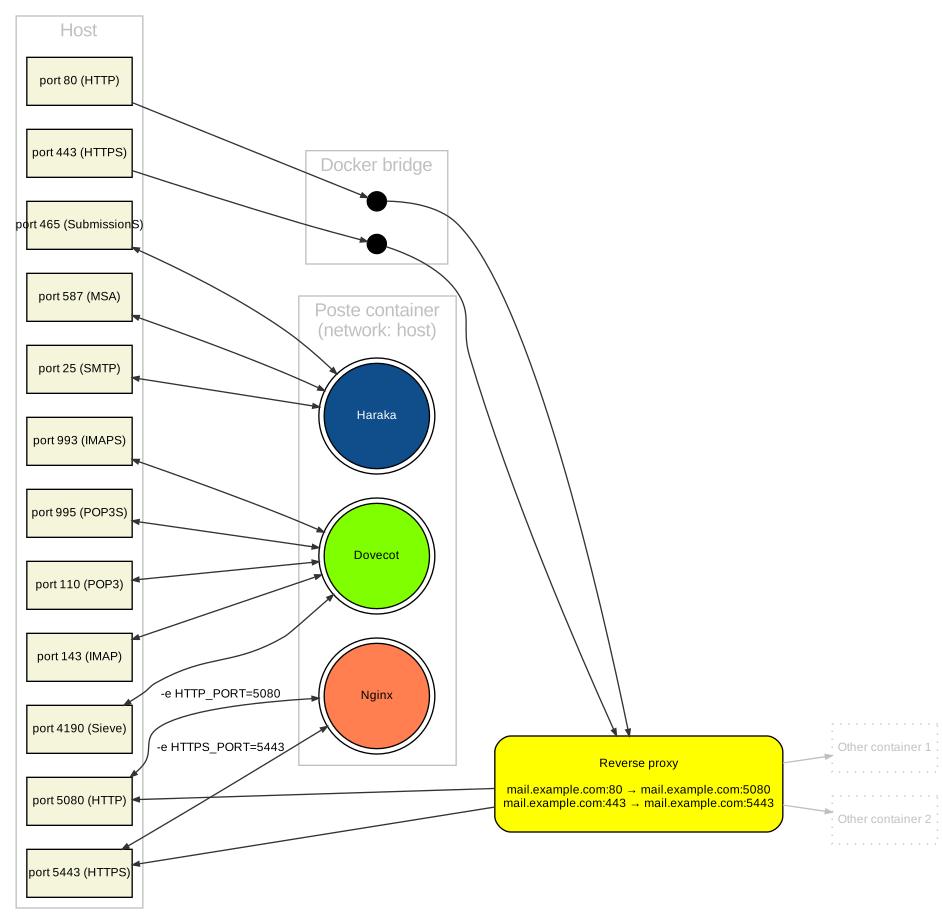
Reverse proxy, poste.io, other web containers and network=host (when you run other HTTP services at same server)
Yes: IPv4 and IPv6 compatible
Caution: administration access IPs might be hidden when using dockerd userland-proxy mode
Note: the host's iptables firewall for port 80 and 443 might require adjust if docker is bridging in iptables mode
Note: Let's encrypt certificates requires "/.well-known" folder properly redirected to poste container
-
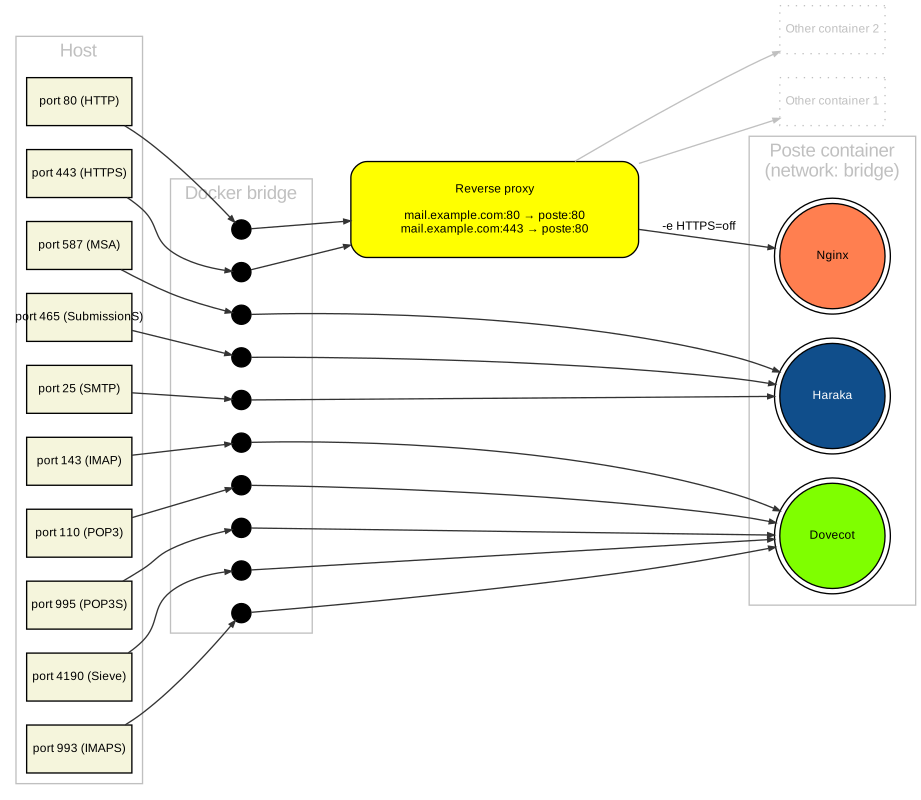
network=bridge (dockerd userland-proxy=false)
Yes: IPv4 compatible
Caution: IPv6 will not work at all by default (the easiest and ugliest solution is to use IPv6 NAT, see: https://palant.de/2018/01/05/getting-published-docker-container-ports-to-work-with-ipv6/ or https://github.com/robbertkl/docker-ipv6nat)
Note: the host's firewall will require adjusting if you want use iptables
Note: Let's encrypt certificates requires "/.well-known" folder properly redirected to poste container
-
network=bridge (dockerd userland-proxy=true)
Do not use: Impossible to set up properly
Do not use: Prone to open relay
Do not use: Multiple SPAM measures will not work